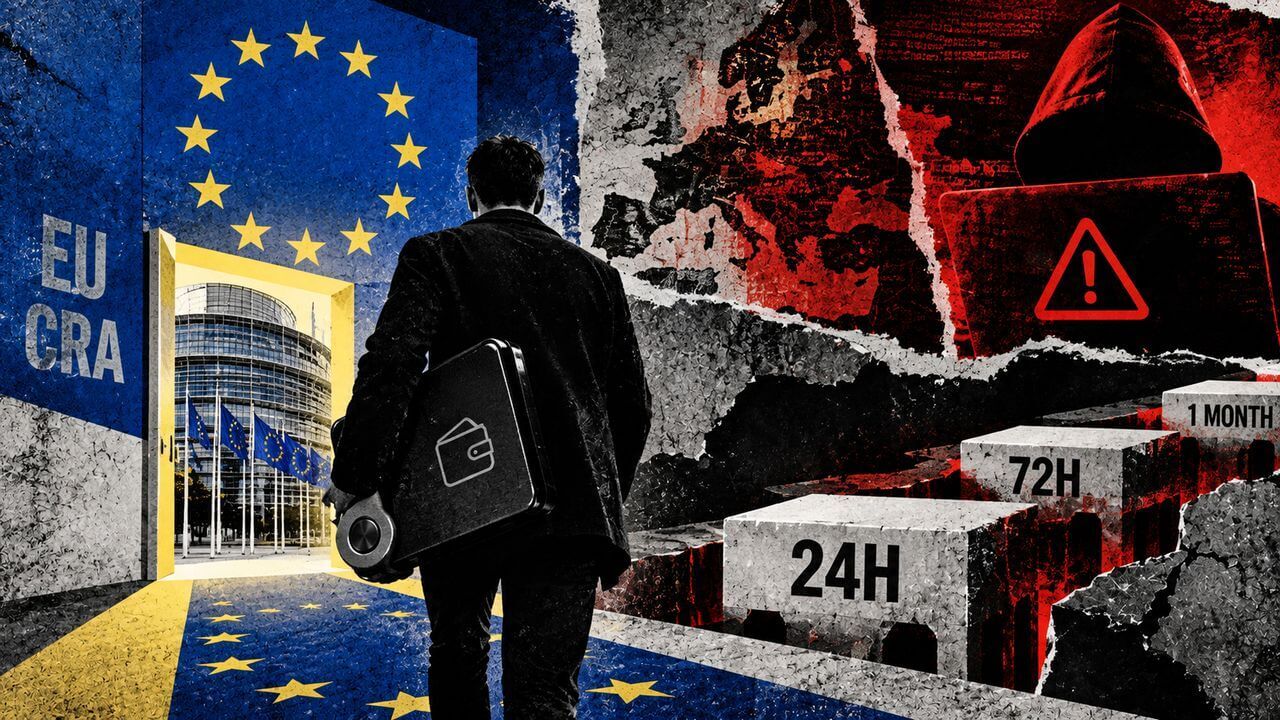
The European Union’s Cyber Resilience Act (CRA) is now in effect, requiring commercial manufacturers of connected hardware wallets or wallet software to report any actively exploited vulnerability or severe security incident to cyber authorities within 24 hours of discovery. This new regulation, which came into force on Sept. 11, 2026, aims to enhance the security and resilience of digital products in the EU market.
According to the European Commission’s reporting guidance, the CRA applies to products with digital elements that are made available on the EU market and have a direct or indirect data connection to a device or network. This includes commercially supplied connected hardware wallets or downloadable wallet apps, although not every wallet brand or service is explicitly mentioned in the guidelines.
Manufacturers must adhere to specific reporting deadlines outlined in the CRA. The initial warning must be submitted within 24 hours of identifying a vulnerability or incident, indicating the member states where the product is available and whether unlawful acts are suspected for severe incidents. A more detailed notification is then required within 72 hours, providing additional information on the product, exploit, vulnerability, and any corrective measures taken.
The final deadline for submitting reports varies depending on the nature of the event. Vulnerability reports must be filed within 14 days of implementing a corrective measure, while severe incident reports are due one month after the initial notification. All reports must be submitted through the Single Reporting Platform launched by ENISA, the EU cybersecurity agency, and shared with relevant national teams.
It’s important to note that the reporting rule applies to in-scope products placed on the market before Dec. 11, 2027, ensuring that existing product lines are also covered by the regulation. Additionally, open-source licensing does not exempt manufacturers from their reporting obligations, with specific guidelines provided for commercially supplied free and open-source products.
Overall, the CRA’s rapid reporting regime aims to improve the security of digital products in the EU market, ensuring timely responses to cybersecurity incidents and vulnerabilities. This regulatory framework sets the stage for broader product-security requirements that will come into effect in the future, emphasizing the importance of proactive security measures in the digital landscape.