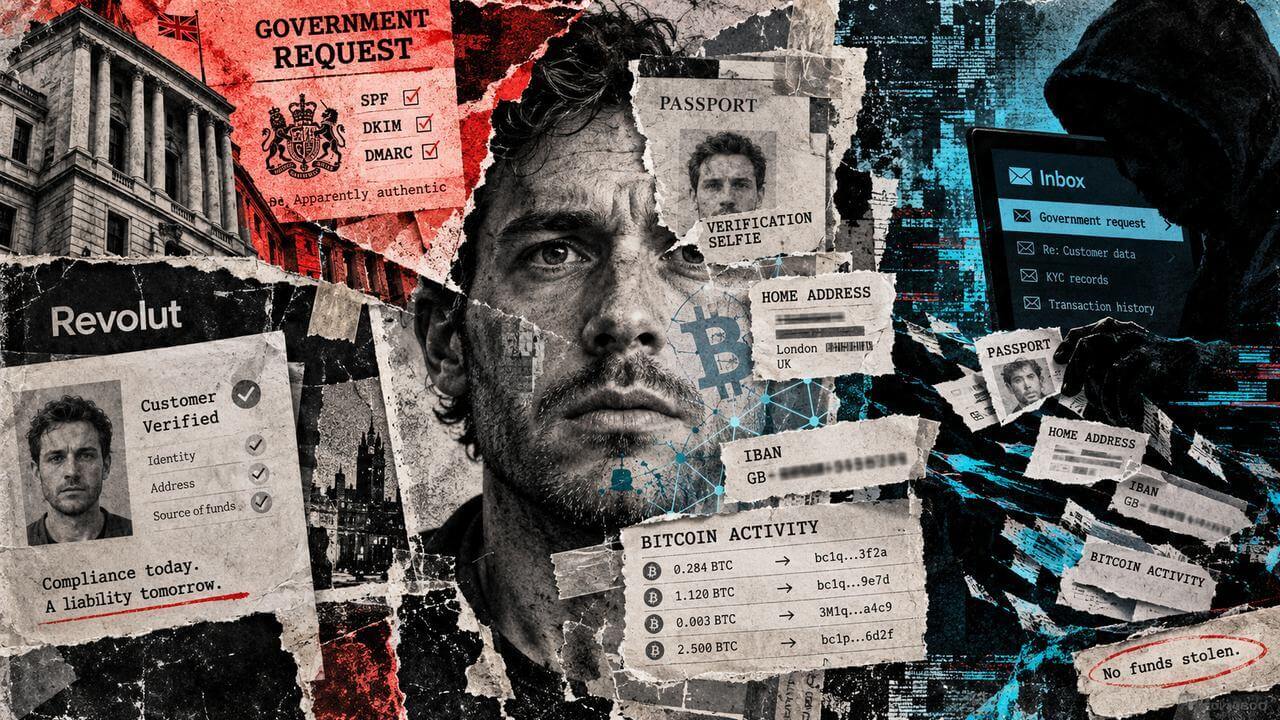
Revolut, a popular fintech platform, recently faced a major data breach that exposed sensitive information of its customers. The breach occurred when Revolut mistakenly treated a fraudulent government request as legitimate, leading to the disclosure of customers’ passports, verification selfies, and Bitcoin transaction histories.
Affected customers were informed that the leaked information could include copies of their passport or driver’s license, verification selfies, personal details such as names, dates of birth, occupations, home addresses, phone numbers, IBANs, and account statements. Additionally, withdrawal records and complete transaction histories, including Bitcoin activity, may have been compromised.
The fraudulent request came from an unauthorized mailbox within the domain infrastructure of a legitimate government agency, carrying valid authentication credentials. Revolut promptly recognized the request as fraudulent, blocked the unauthorized address, and initiated the process of notifying affected customers and regulatory authorities. However, the company has refrained from disclosing the identity of the agency involved or the exact number of customers impacted by the breach.
This incident has sparked concerns about the extent of information financial institutions collect from customers and the protocols in place when government agencies seek access to these records. The incident also highlighted the tension between compliance requirements and customer privacy. Banks and fintech firms gather extensive identity and transaction data to comply with regulations like know-your-customer and anti-money laundering policies. This sensitive data becomes even more critical when it links verified identities to cryptocurrency transactions.
For Bitcoin holders, the exposed records could potentially provide attackers with more than just financial information. Since Bitcoin transactions are recorded on a public blockchain, linking a known individual to specific activities can help map out their broader on-chain footprint, posing a significant risk to customer privacy and security.
The breach also raised questions about the verification process Revolut follows for government requests. The fraudulent email managed to bypass authentication mechanisms like SPF, DKIM, and DMARC, designed to verify the legitimacy of sender domains. This suggests that the attacker had unauthorized access to the government agency’s email infrastructure, rather than simply spoofing the sender information.
Former Mt. Gox CEO Mark Karpelès emphasized the importance of identifying the compromised government agency to help other financial institutions assess whether they also received similar fraudulent requests. Revolut is currently investigating the incident and has not disclosed the agency’s identity.
Moving forward, it is crucial for Revolut and other financial institutions to reassess their verification processes for government requests and implement additional security measures to prevent such breaches in the future. Customer trust and data security should remain top priorities to safeguard sensitive information from unauthorized access.