
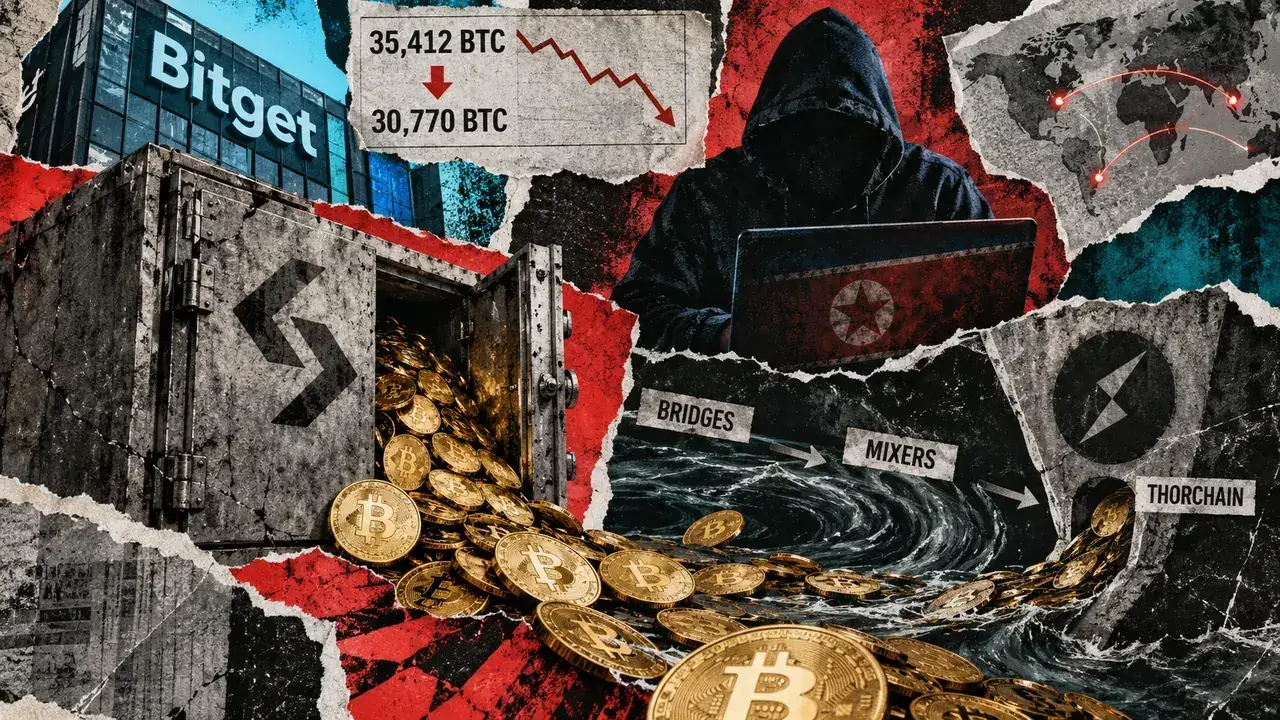
Nearly 5,000 Bitcoin has left Bitget’s tracked reserves after the crypto exchange reopened withdrawals following its $387.5 million hack.
Bitget Chief Executive Officer Gracy Chen announced that the exchange had processed 9,585 withdrawal orders totaling 4,098.036 BTC as of 17:00 UTC+8, shortly after resuming Bitcoin withdrawals.
DeFiLlama data showed Bitget’s tracked Bitcoin balance falling to about 30,770 BTC from 35,412 BTC, a decline of roughly 4,642 BTC, equivalent to about $391 million at current prices.
The reserve decline exceeds the amount Chen mentioned Bitget had processed through customer withdrawal orders. DeFiLlama tracks assets held in wallets attributed to exchanges, meaning changes can also reflect wallet movements or differences in address coverage rather than customer withdrawals alone.
The rapid outflow provides the first insight into how users are reacting after Bitget froze withdrawals for four days while investigating the largest security incident in its eight-year history.
Bitget resumed Bitcoin withdrawals on Sept. 28 after completing additional checks on its withdrawal infrastructure. Ethereum withdrawals are set to follow on Sept. 29, USDT on Sept. 30, and remaining tokens, fiat, and peer-to-peer services on Oct. 2.
The restart comes as Bitget aims to reassure customers that the attack did not compromise its private keys or cold-wallet reserves.
Chen explained that attackers exploited vulnerabilities in third-party products to obtain internal credentials, which were then used to submit fraudulent withdrawal instructions bypassing Bitget’s risk controls. The exchange has isolated affected systems, reissued internal credentials, and restructured access to sensitive infrastructure. Bitget also disabled the affected third-party functionality while waiting for a fix from the vendor.
Blockchain security firms Mandiant and SlowMist are assisting with forensic analysis and attempts to trace the stolen assets. Bitget assured customers that they will not suffer losses from the incident, and the Protection Fund will cover the shortfall. The company plans to replenish the fund with its own capital to over $300 million within a week.
Meanwhile, recovering the stolen Bitget funds is becoming more challenging as the assets are fragmented across bridges, cross-chain protocols, and privacy services.
Blockchain investigator ZachXBT reported that Chinese illicit actors were laundering proceeds from the exploit on behalf of hackers allegedly linked to North Korea. Funds were being chain-hopped and deposited into mixing services, including Wasabi.
ZachXBT linked one participant in the laundering network to movements following the $292 million Kelp DAO exploit earlier this year, stating that he observed similar behavior after attacks attributed to the TraderTraitor campaign.
The laundering activity has put THORChain in the spotlight regarding whether permissionless infrastructure should intervene when stolen assets pass through its systems. THORChain stated that it would not selectively block wallets or swaps, arguing that its role is akin to censorship-resistant networks like Bitcoin and Ethereum.
However, blockchain security firm GoPlus challenged that comparison, claiming that THORChain’s architecture gives its node operators powers that base-layer validators do not have. GoPlus pointed out THORChain’s emergency controls used during its own $10.7 million exploit in May, suggesting a similar framework could be applied against addresses linked to the Bitget attackers.
THORChain argued that a network halt is meant to protect the protocol itself and differs from selectively censoring a specific user, wallet, or swap. The protocol maintained neutrality even when known stolen funds transacted through it.
GoPlus accused THORChain of benefiting financially from this stance, estimating that significant amounts of BTC and XRP had already exited through the protocol from the Bitget exploit. The firm also highlighted THORChain’s role in laundering proceeds from the 2025 Bybit hack, creating an incentive conflict when node operators decline to interfere with illicit flows.
The industry now faces the question of whether decentralized protocols with emergency controls should remain transaction-neutral when used to launder funds from major hacks.
As Ethereum, USDT, and other withdrawals reopen, investigators are working to recover assets fragmented across chains and routed through infrastructure whose operators may refuse to intervene. The ongoing debate surrounding the handling of stolen funds in decentralized protocols continues to evolve.