
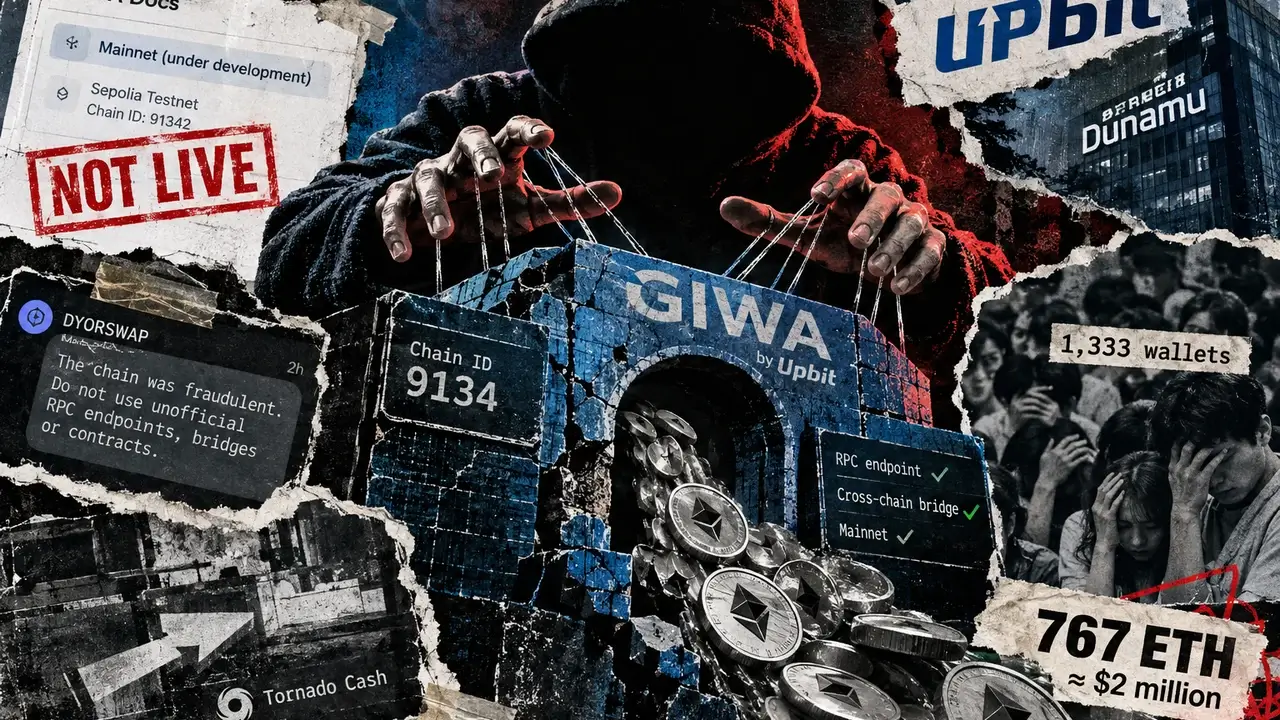
Scammers recently created a fake version of the GIWA blockchain, which is backed by Upbit, and managed to deceive 1,333 wallets into depositing a total of 767 ETH, valued at around $2 million. The fraudulent network appeared to be the anticipated Ethereum Layer 2 mainnet for GIWA, complete with an RPC endpoint, cross-chain bridge, and Chain ID 9134, which is associated with the upcoming launch. However, the actual GIWA mainnet was not operational at the time of the scam.
In response to the incident, GIWA clarified that there was no production RPC that had been leaked, as the mainnet RPC was still in development. The documentation only listed GIWA Sepolia, which uses Chain ID 91342. DYORSWAP, whose community initially engaged with the fake network, later confirmed that the chain was indeed fraudulent and cautioned users against unofficial RPC endpoints, bridges, and contracts.
The operator of South Korea’s largest crypto exchange, Upbit, Dunamu, is developing GIWA using Optimism’s OP Stack. It was announced in May that GIWA is set to be the first Self-Managed OP Enterprise chain, allowing Upbit to maintain operational control while receiving infrastructure and support from Optimism.
The attackers behind the scam waited for significant deposits before making changes to the bridge. On-chain data indicated that the attackers prepared the infrastructure for hours before the initial deposits were made. Wallets tied to the operation were funded through ChangeHero on September 26, and about 11 hours later, the Safe wallet controlling the scheme and the fake bridge went live. Over the following 13 hours, 1,333 wallets deposited a total of 767 ETH.
After the deposits were made, the operators altered the bridge’s portal code and drained 766 ETH in a single transaction. The attack exploited the use of Chain IDs to make the environment seem legitimate while controlling the infrastructure receiving user funds. The stolen funds have since started moving, with some ETH being routed through Tornado Cash, making it harder to trace. Most of the stolen funds are still visible on-chain, but further transfers could complicate recovery efforts.
In response to the scam, DYORSWAP has offered 40% compensation to smaller victims who bridged less than 5 ETH. Claims involving more than 5 ETH will be handled separately, with identity and address verification required. The project has urged victims to verify compensation addresses through official channels to avoid falling for fake reimbursement requests. Losses for users are still significant, even with approved claims, as smaller victims will only recover a fraction of their deposits.
DYORSWAP is maintaining records of RPC, bridge addresses, transaction data, and community communications to assist investigators in reconstructing how the fraudulent network spread. The incident serves as a reminder for users to exercise caution and verify the authenticity of blockchain networks before engaging with them.