
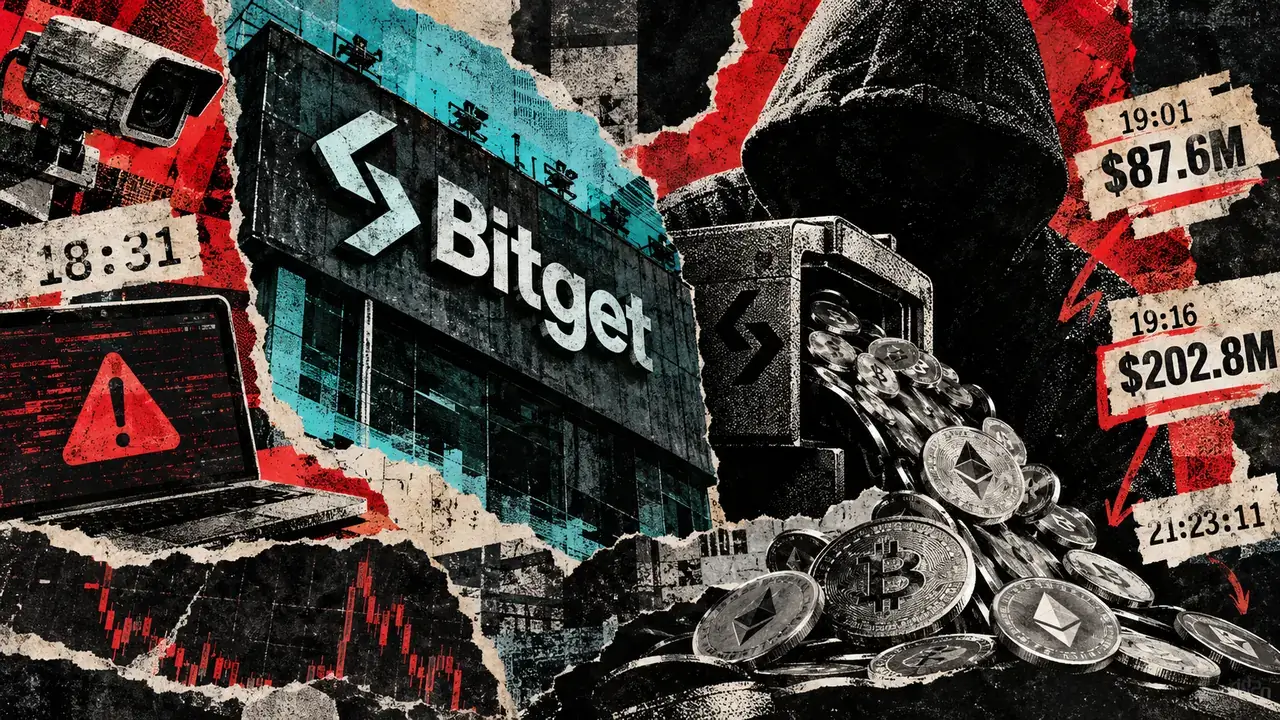
Bitget, a popular crypto exchange, recently experienced a major security breach that resulted in the loss of hundreds of millions of dollars. The breach involved unauthorized wallet transfers, with attackers draining a total of $387.5 million from Bitget’s hot and warm wallets.
The incident began when Bitget’s systems detected unauthorized transfers at 18:31 UTC on Sept. 24. Despite activating emergency protocols immediately, the attackers were able to move $87.6 million from hot wallets at 19:01 and another $202.8 million from warm wallets at 19:16. These transfers happened within a span of 24 seconds, accounting for a significant portion of the total stolen funds.
Hypernative, a blockchain security firm, conducted a reconstruction of the attack and found that the attacker initially tested the compromised route with small transfers before escalating to larger amounts. The attacker exploited a vulnerability in Bitget’s backend system, spoofed withdrawal data, and tricked the exchange’s authorization process into approving the transfers without compromising private keys.
The security firm identified several control measures that could have potentially stopped the attack after the initial alert. These measures include checks to ensure that every signed transfer corresponds to an independently stored customer withdrawal or approved treasury transaction, comparing transaction parameters against normal withdrawal pipeline parameters, implementing velocity limits on wallet transfers, and automatically suspending affected signers in case of anomalous transfer alerts.
Despite Bitget’s efforts to contain the breach and remediate the vulnerability, the compromised signing route remained operational for several hours after the initial alert, allowing the attackers to continue moving funds until 21:23 UTC. Bitget has since stated that no further unauthorized transfers occurred after containment and continues to work with cybersecurity firms Mandiant and SlowMist on the forensic investigation.
The incident raises questions about Bitget’s security response and why the compromised route was not shut down sooner to prevent the substantial loss of funds. Moving forward, it is crucial for crypto exchanges to strengthen their security measures and response protocols to prevent similar breaches in the future.