
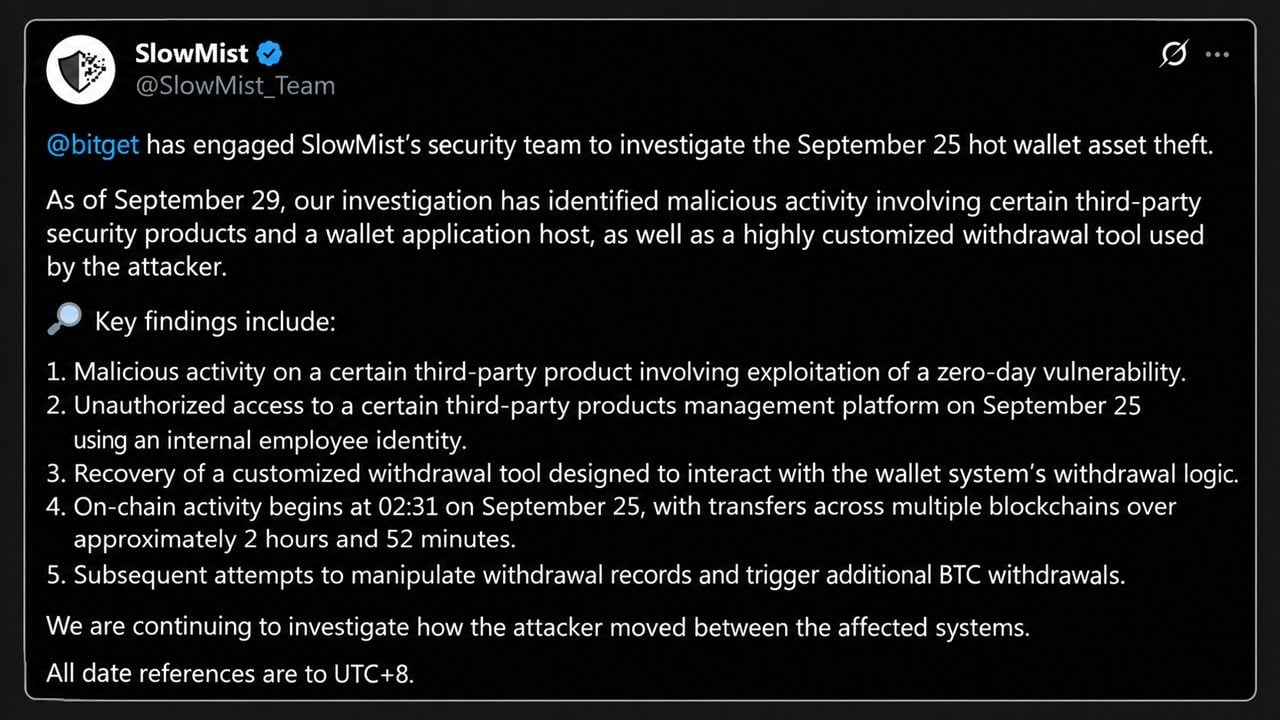
The recent security breach at Bitget has sent shockwaves through the cryptocurrency world, with Slowmist, a blockchain security firm, uncovering key details about the attack that have reshaped the timeline of events. The investigation revealed that the door to the hackers was open since August, when a zero-day vulnerability in a third-party security product allowed them to gain access to Bitget’s systems.
According to Slowmist’s findings, the attackers exploited an employee’s identity and a custom withdrawal tool to move funds for nearly three hours on the night of the theft. The report details the minute-by-minute sequence of events, showing how the attackers used a highly customized withdrawal tool to forge risk-control parameters and trigger the withdrawal process. In just 18 minutes, $228 million was siphoned off across seven different chains, with XRP accounting for the largest portion.
The stolen funds are still in motion, with suspected North Korean hackers using the CoW Protocol and Chainflip to launder the money. Despite efforts by various platforms to block the flow of funds, the hackers have been successful in evading detection and moving the stolen assets into bitcoin.
Bitget has reassured its users that the User Protection Fund, holding over $464 million, will cover the losses incurred from the theft. Withdrawals are gradually being restored, starting with bitcoin and followed by other assets. However, the bigger question remains unanswered – how did the attackers manage to move between systems and evade detection for so long?
The implications of this security breach are far-reaching, with other exchanges potentially at risk if they are running similar security stacks. The need for heightened security measures and constant vigilance in the face of sophisticated cyber threats has never been more apparent. As the investigation continues, it is crucial for all cryptocurrency platforms to review their security protocols and ensure that they are equipped to withstand potential attacks.
In conclusion, the Bitget security breach serves as a stark reminder of the ever-present dangers in the cryptocurrency world. By learning from this incident and implementing robust security measures, exchanges can better protect themselves and their users from malicious actors seeking to exploit vulnerabilities in the system.